
The fastest way to get CISSP Certified. Join our bootcamp

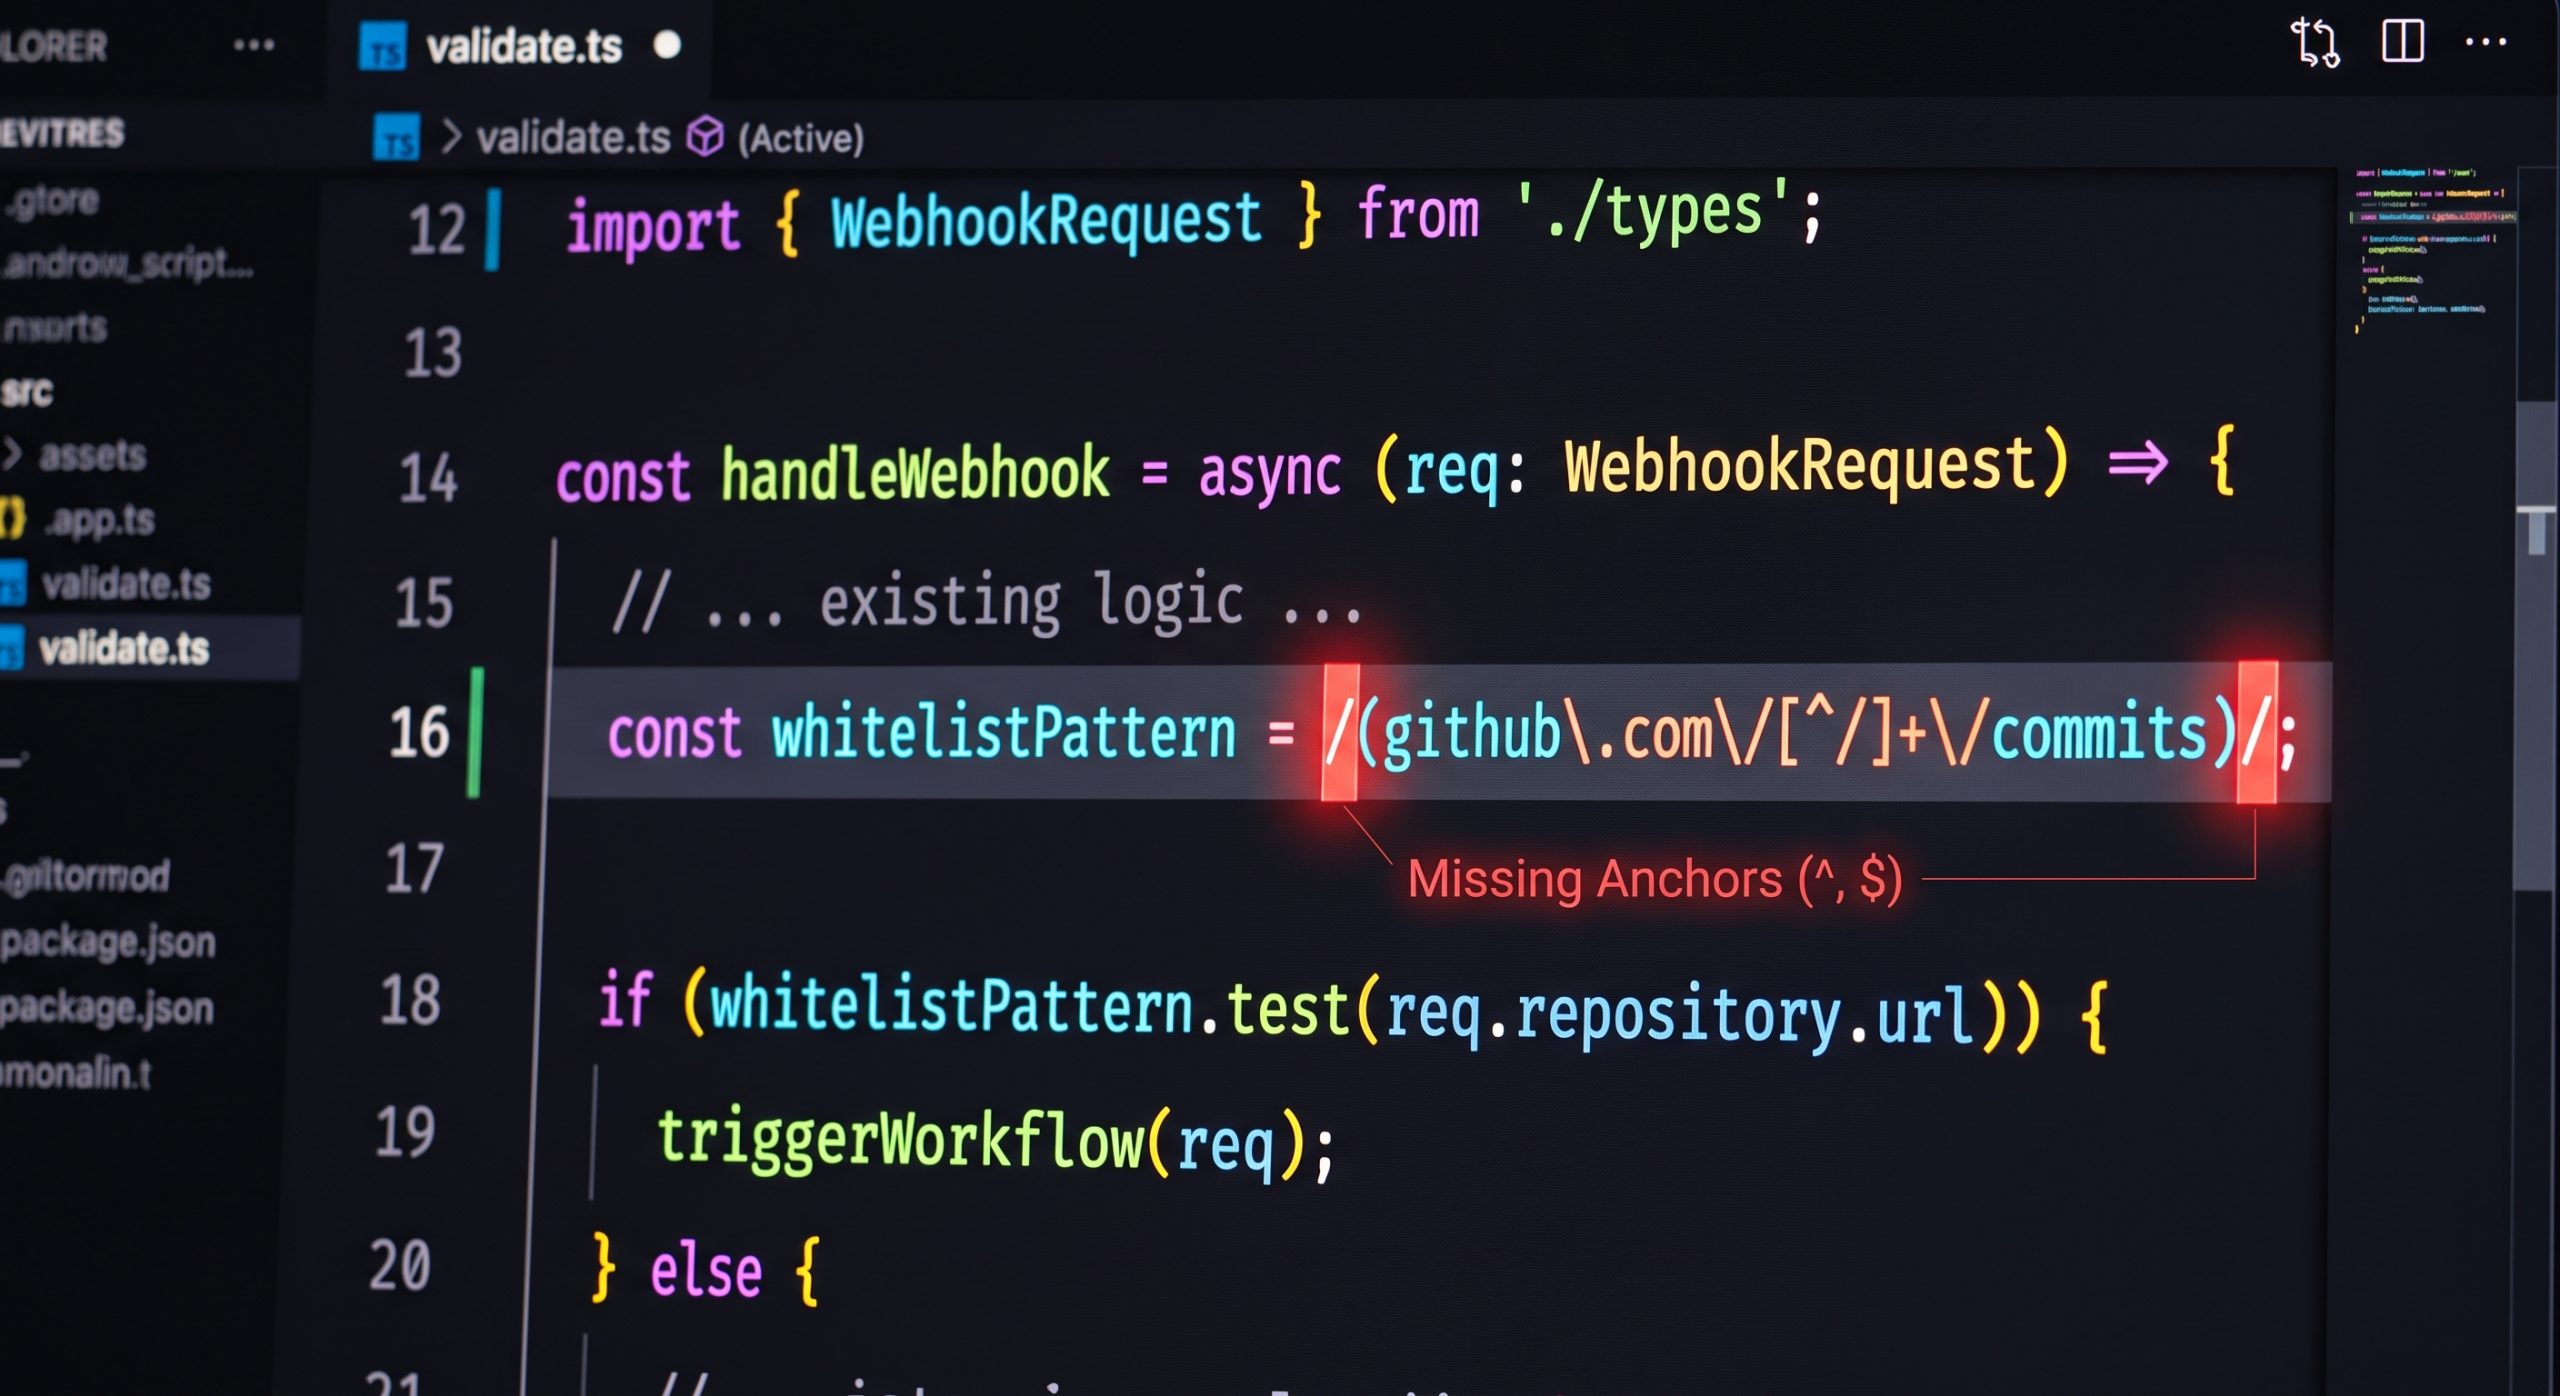
August 2025. Security researchers at Wiz discovered a misconfiguration in AWS CodeBuild, the service AWS uses to manage its own open source projects.
The misconfiguration was a missing anchor in a webhook filter. A single regex error.
That error meant an unauthenticated attacker could bypass AWS's security checks using standard developer workflows. Fork a repository. Submit a pull request. The kind of thing any intermediate developer does every day.
What made this alarming wasn't the sophistication of the attack. It was what it could reach.
The misconfiguration exposed AWS's own JavaScript SDK repository. That SDK powers the AWS Management Console and is installed in roughly 66% of cloud environments worldwide. An attacker who gained access could have injected malicious code into the SDK, which would then propagate through AWS updates to every environment running it.
Wiz's researchers called it potentially bigger than SolarWinds.
AWS fixed the issue within 48 hours of disclosure. No customer environments were impacted. But the disclosure, which came publicly in January 2026, revealed something worth sitting with: a single misconfiguration in a CI/CD pipeline, introduced by the people who build the cloud platform itself, nearly created a supply chain attack that could have reached two-thirds of all cloud environments globally.
The lesson isn't about AWS.
AWS responded quickly, fixed the issue, and introduced new hardening measures. The lesson is about the nature of cloud security risk.
Cloud environments are connected in ways that aren't always visible. Your security posture depends not just on your own configurations, but on the configurations of every service you depend on, every pipeline those services use, and every dependency those pipelines pull from.
The shared responsibility model tells you what you're responsible for in your cloud environment. It doesn't account for supply chain risk that originates upstream from your environment entirely.
This is what makes cloud security genuinely different from traditional security. The perimeter isn't yours to control. Dependencies run deep. A single misconfiguration several layers removed from your own environment can become your problem without warning.
CCSP is built around this reality.
Not just cloud security concepts, but how to think about risk in environments where your attack surface extends far beyond what you directly manage. Cloud architecture and design, supply chain security, identity and access management in cloud environments, and incident response when the threat enters through a dependency you didn't know you had.
Our next CCSP Bootcamp runs October 12-16. Five days with John Berti and Kelly Handerhan, who co-developed the official ISC2 CCSP certification materials. You get everything you need to pass, plus full MasterClass access for your final review.
The CCSP exam moved to a new outline on August 1, 2026. Our materials are fully updated to match it.
Best,
The DestCert Team
P.S. Can't make the bootcamp? Our CCSP MasterClass covers the same material at your own pace.
Free CISM MindMap: Business Continuity Management
We put together a free MindMap video covering the key concepts in Domain 4, a quick, clear way to get the big picture before you dive into studying. Free to watch, no strings attached. Plus you'll get downloadable audio files and printable PDFs.
Almost time to let the CAT out
We've been building something. You'll see it soon.
Destination AAISM: The Complete Guide is here
$2.99 this week only. All three AAISM domains covered, built the same way we write our CISSP and CCSP guides: heavy on diagrams, light on filler. Buy this week and email your receipt to books@destcert.com for a shot at a free Essential AAISM MasterClass.

Destination CCSP just got a major update
We've refreshed the guidebook to match the latest exam outline, with AI/ML security now woven through all six domains. Same clear explanations that have helped thousands pass, updated for what ISC2 tests today.